22 Aug Cybersecurity Audit Los Angeles: Navigating 2026 Compliance and Protection
In 2026, a cybersecurity audit in Los Angeles is no longer a voluntary best practice for the tech and entertainment sectors. It’s a mandatory regulatory defense strategy against the California Privacy Protection Agency. With US cybercrime losses exceeding $20 billion last year, the stakes for your business have never been higher. You’re likely feeling the weight of potential CalPrivacy enforcement actions or confusion over the latest CCPA audit triggers. It’s exhausting to stay vigilant against sophisticated ransomware while trying to decipher complex legal mandates.
We understand that your goal isn’t just to check a box, but to achieve true stability and peace of mind. This article provides a clear roadmap for vulnerability remediation and full regulatory compliance. We’ll show you how to master California’s new requirements and secure your Los Angeles business against modern threats using an expert-led framework. By the end of this overview, you’ll have a strategic plan to transform these technical anxieties into a competitive edge, ensuring your organization remains a step ahead of both hackers and auditors.
Key Takeaways
- Learn why the California Privacy Protection Agency now requires mandatory audits for businesses handling sensitive data in 2026.
- Discover how a professional cybersecurity audit los angeles integrates technical assessments with policy reviews to meet state mandates.
- Understand the necessity of independent auditing to fulfill CalPrivacy certifications and maintain objective security standards.
- Follow our five-step preparation framework to inventory your data and identify critical security gaps before the deadline.
- Explore how a fixed-price IT model helps you manage compliance costs while providing a proactive defense against modern threats.
The 2026 Cybersecurity Landscape in Los Angeles: Why Compliance is Mandatory
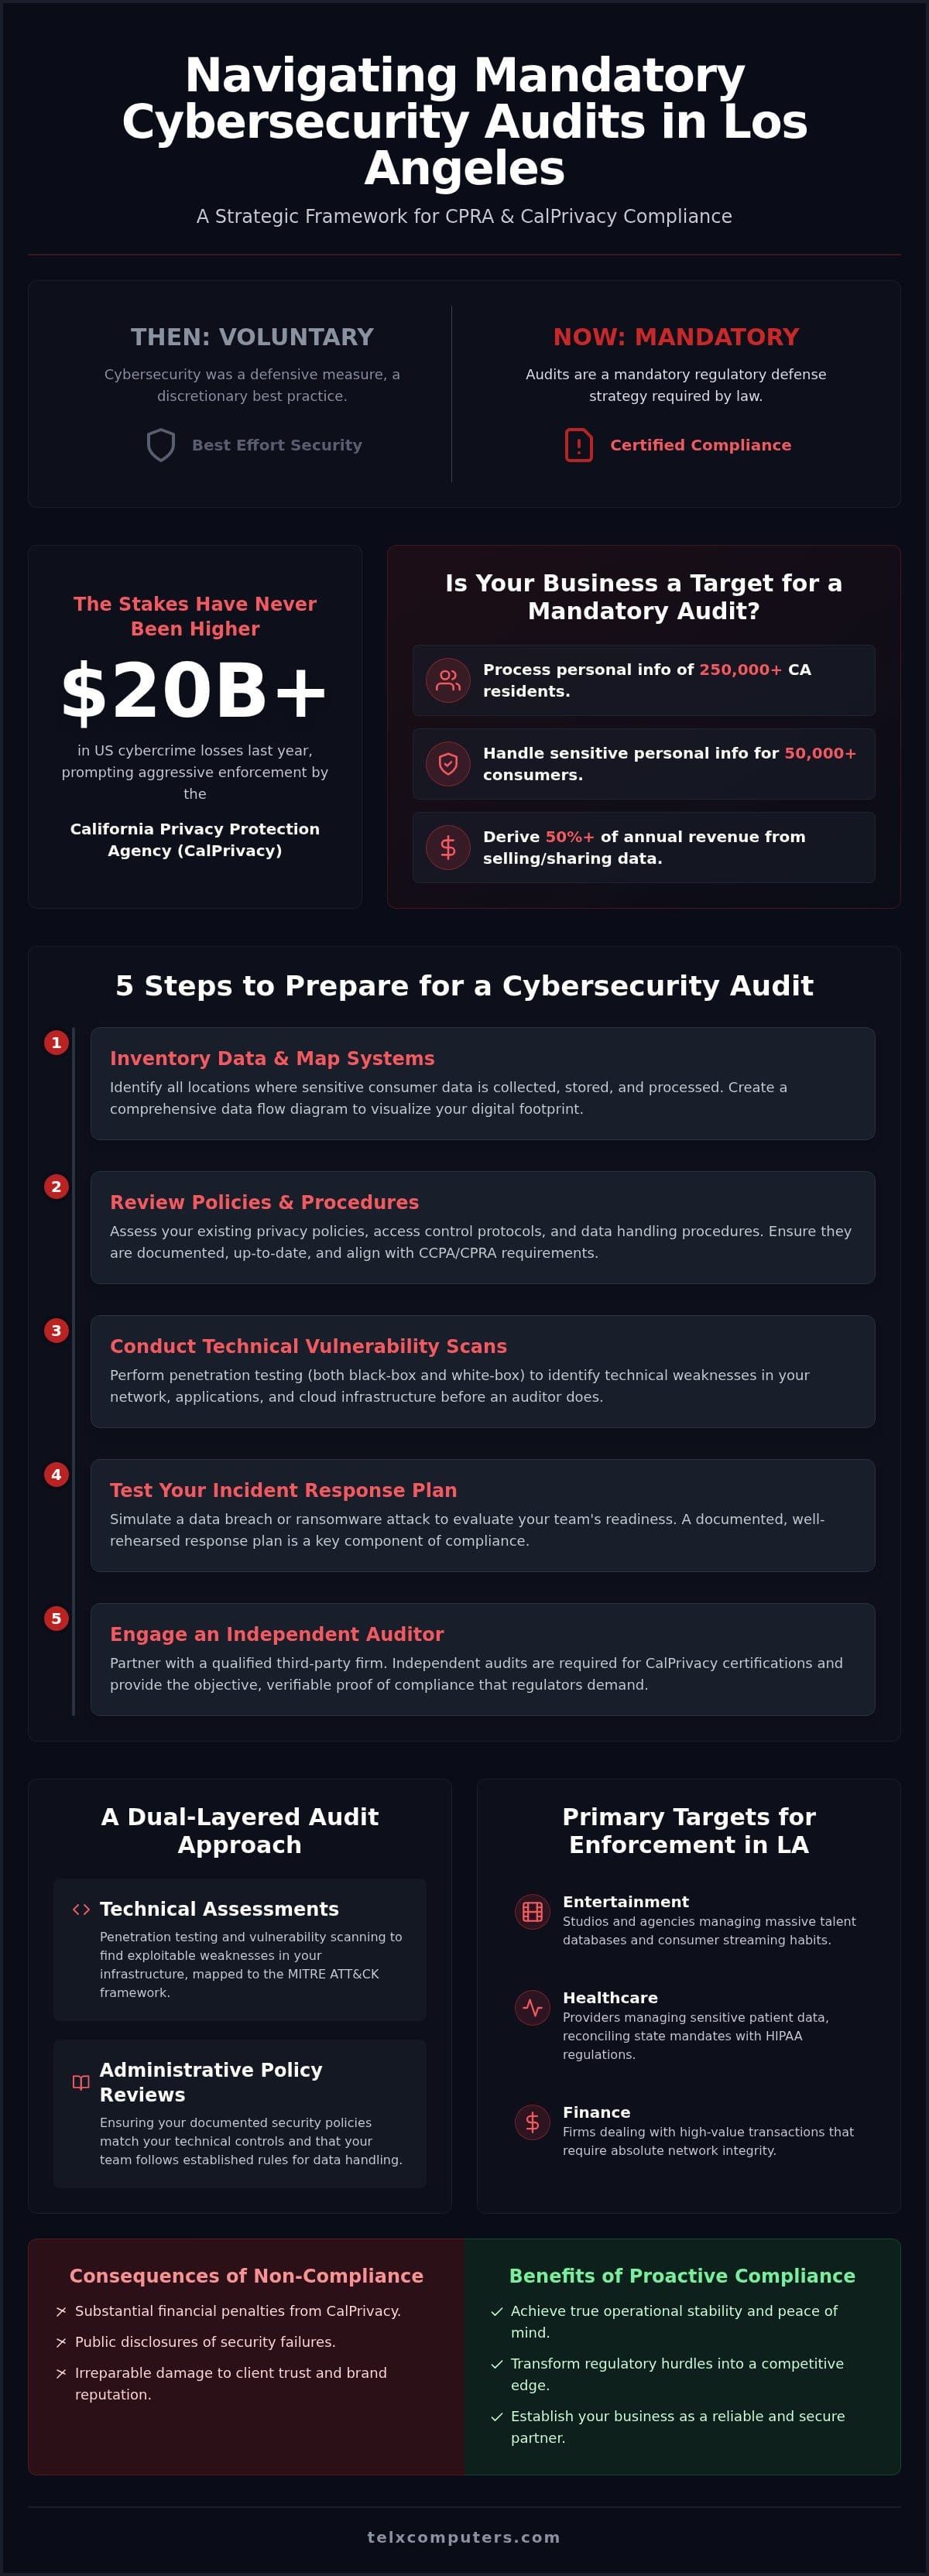
For years, many businesses viewed digital security as a defensive measure rather than a legal requirement. In 2026, that landscape has shifted fundamentally. A cybersecurity audit los angeles is now a mandatory regulatory defense strategy for organizations operating in the region’s high-stakes sectors. This change stems from the aggressive expansion of the California Privacy Protection Agency (CalPrivacy), which recently established its dedicated Audits Division to enforce the latest iterations of the CCPA and CPRA. The shift from “best effort” security to “certified compliance” under Article 9 of the CCPA means your security protocols must now be documented, verified, and legally defensible.
Understanding the CalPrivacy Audits Division
The formation of the Audits Division in early 2026 introduced the role of the Chief Privacy Auditor. This official oversees rigorous examinations of business practices to ensure total data integrity across the state. The division identifies “significant risk” businesses for examination based on how they handle consumer profiles. If your organization uses automated decision-making technology or processes sensitive biometric data, you’re likely on their radar. The CalPrivacy mandate is the new standard for California data privacy in 2026. A professional information security audit is no longer just a technical checkup; it’s a comprehensive review designed to prove that your technical controls match your written privacy policies.
Los Angeles Regulatory Triggers
Specific thresholds determine if your business must undergo these mandatory annual reviews. Currently, the requirements apply to businesses that process the personal information of 250,000 or more California residents. However, the volume isn’t the only trigger. If your firm handles sensitive personal information for 50,000 or more consumers, or derives half of its annual revenue from selling or sharing data, the audit mandate applies. Los Angeles firms in entertainment, healthcare, and finance are primary targets for enforcement due to the high value of the data they manage.
- Entertainment: Studios and agencies managing massive talent databases and consumer streaming habits.
- Healthcare: Providers must reconcile state mandates with existing healthcare IT services and HIPAA regulations.
- Finance: Firms dealing with high-value transactions that require absolute network integrity.
The consequences of non-compliance are severe. Beyond substantial financial penalties, the Audits Division can initiate public disclosures of security failures. These public records can cause irreparable damage to client trust and brand reputation. Transitioning to a model of proactive compliance isn’t just about avoiding fines; it’s about establishing your business as a reliable, secure partner in a volatile digital economy. We position ourselves as an extension of your team to ensure these regulatory hurdles don’t slow your momentum.
Core Components of a Professional Cybersecurity Audit
A professional cybersecurity audit los angeles isn’t just a simple checklist. It’s a dual-layered approach that bridges the gap between regulatory compliance and actual technical defense. You need technical vulnerability assessments to find the holes and administrative policy reviews to ensure your team follows the rules. This holistic view aligns with the GAO Cybersecurity Program Audit Guide, which emphasizes that security is as much about documented processes as it is about high-end software.
Technical Penetration Testing
We use penetration testing to simulate real-world attacks and identify where your perimeter might crumble. Black box testing assumes no prior knowledge of your system, mimicking an outside hacker’s perspective. White box testing provides full transparency, allowing for a deep dive into your internal architecture. We map these results to the MITRE ATT&CK framework. This ensures your remediation efforts target the specific tactics, techniques, and procedures that modern attackers use. If we find gaps in your network perimeter, implementing robust ransomware protection becomes the immediate priority for your remediation roadmap.
Your audit must also scrutinize core network infrastructure. We analyze firewalls and VPNs while transitioning your team toward a zero-trust architecture. For Los Angeles teams relying on remote work, cloud security auditing is vital. We secure Microsoft 365 and AWS environments to prevent unauthorized data exfiltration. If you’re unsure where your current infrastructure stands, you can get an instant quote to see how we can begin securing your digital assets.
Data Governance and Privacy Controls
Data is your most valuable asset, and it’s what CalPrivacy auditors care about most. We audit encryption protocols for data both at rest and in transit. A critical part of this review involves access control. We help you implement the Principle of Least Privilege (PoLP). This ensures users only have the access necessary for their specific roles, which limits the “blast radius” of a potential breach. Finally, we evaluate third-party vendor risks. Your security is only as strong as the weakest link in your supply chain, making vendor management a non-negotiable part of the 2026 landscape.
The human element is often the hardest to secure, yet it’s frequently the primary entry point for breaches. We conduct social engineering tests and phishing simulations to evaluate staff awareness. These tests identify which employees need more training before a real threat arrives. By testing your team in a controlled environment, we transform them from a liability into a proactive line of defense.
Internal vs. External Audits: The Importance of Independence
CalPrivacy regulations in 2026 emphasize a crucial distinction: the need for independence. While internal IT teams perform vital daily maintenance, they cannot provide the objective verification required for high-level certifications. Self-auditing complex LA IT infrastructures often leads to an inherent conflict of interest. It’s difficult for any team to identify systemic flaws in a network they built and maintain themselves. This is why a third-party cybersecurity audit los angeles is essential for maintaining your legal and regulatory standing.
The Role of Certified Auditors (CISA/CISSP)
Legal defensibility in Los Angeles courts often hinges on the credentials of the professional performing the review. Certified Information Systems Auditors (CISA) or Certified Information Systems Security Professionals (CISSP) provide the professional authority needed to satisfy state regulators. These experts evaluate your systems against rigorous frameworks like the NIST security and privacy controls. Independent audits provide the unbiased lens necessary for true risk mitigation. By using an external validator, you build significant trust with stakeholders and clients who demand proof of your technological edge.
Bridging the Gap with Managed IT
While an external auditor identifies the gaps, a strategic ally like Telx Computers closes them. We act as the bridge between audit findings and actual network security. Using our Managed IT Support Service provides the foundation for audit readiness. We don’t just hand you a report; we implement the fixes. Having an LA-based team allows for rapid on-site remediation. This ensures that physical security flaws or hardware-level vulnerabilities are addressed immediately rather than weeks later. We serve as an extension of your team, ensuring that audit recommendations result in concrete business outcomes.
Proactive auditing is an investment in your business’s continuity. The average cost of a data breach in the United States reached $10.22 million in 2025. Compare that to the manageable cost of an annual audit and ongoing managed support. Reactive breach response is chaotic, expensive, and damaging to your reputation. Proactive measures replace that anxiety with a sense of stability. We position ourselves as your silent engine, ensuring your compliance is handled with professional efficiency so you can focus on your organization’s growth.
5 Steps to Prepare Your LA Business for a 2026 Audit
Preparation is the difference between a seamless certification and a costly enforcement action. In 2026, the California Privacy Protection Agency expects your organization to have a mature, documented security posture. Relying on a last-minute scramble won’t satisfy the new Audits Division. A successful cybersecurity audit los angeles requires a methodical approach that starts with a preliminary gap analysis of your current data policies. By identifying where your defenses fall short of Article 9 requirements now, you can remediate vulnerabilities before an official examiner arrives.
Inventorying Your Data Assets
You can’t protect what you can’t see. Your second step is to inventory all personal information (PI) processing activities. This involves identifying exactly where consumer data “lives,” whether it’s on a physical server in your Los Angeles office or across various cloud platforms. We help you classify this data based on sensitivity and regulatory impact. A critical part of this process is cleaning up “dark data”—the forgotten, unmanaged information that often clutters corporate networks. Reducing your data footprint directly shrinks your audit scope and minimizes potential liability.
Testing Disaster Recovery
Resilience is a primary focus for 2026 auditors. It’s not enough to have a backup; you must prove it works. Step three involves updating and testing your disaster recovery and business continuity plans. We recommend simulating a total network failure in a controlled environment to verify your recovery time objectives (RTO). Our Servers & Monitoring Systems ensure that your backup integrity remains high and that your systems stay online when it matters most. Auditors will look for evidence that these tests occur regularly and that the results inform your security strategy.
The final stages of preparation focus on the human and strategic elements of your organization. Step four is the formalization of employee security awareness training. You must document that every staff member understands their role in protecting data. Finally, step five is securing an independent partner with local LA expertise. Choosing a strategic ally who understands the specific threats targeting the tech and entertainment sectors ensures your cybersecurity audit los angeles is handled with professional authority. We act as an extension of your team, providing the stability and reliability you need to face regulatory scrutiny with confidence.
Ready to secure your compliance roadmap? Get an instant quote today to see how our fixed-price plans can manage your audit readiness.
Telx Computers: Your Strategic Ally for LA Cybersecurity
Telx Computers has served as a technological pillar for the regional business community since 2002. We don’t just provide a service; we act as an expert guardian for your organization. Successfully completing a cybersecurity audit los angeles requires more than just technical knowledge. It demands a strategic ally who understands the operational pulse of Southern California. Our physical office in Los Angeles ensures that when you need rapid on-site support, we’re already on the ground. We replace technical anxiety with stability by offering fixed-price, unlimited service plans. This model removes the fear of spiraling compliance costs, allowing you to focus on your core business growth while we handle the complexities of CalPrivacy mandates.
The Telx Advantage in Los Angeles
Our approach is rooted in proactive monitoring. We identify vulnerabilities before an official auditor ever sets foot in your office. You gain direct access to our leadership team for strategic compliance consulting, ensuring your security measures align with your long-term goals. This level of personalized attention is why we’re considered an extension of your own team. Our 24/7 help desk is always active, providing a silent engine of efficiency that keeps your staff productive. We understand the specific threats facing the tech and entertainment sectors in LA, from sophisticated ransomware to data exfiltration attempts.
Beyond the Audit: Continuous Protection
A one-time audit is only the beginning of a secure 2026. Threats evolve, and so do California’s regulations. We create customized security roadmaps that adapt to new technical environments and legal requirements. This holistic strategy ensures that your defense isn’t just a series of disconnected fixes but a unified shield. By integrating security into your broader business strategy, we help you leverage compliance as a mark of reliability for your clients. We take pride in being the silent engine behind your success, providing a technological edge that keeps you one step ahead of potential threats.
Ready to secure your organization’s future? Request an Instant Quote for Your LA Cybersecurity Audit and let us build your defense together.
Achieving Stability Through Strategic Compliance
The regulatory landscape of 2026 demands more than just basic firewalls; it requires a documented, verified commitment to data integrity. It’s about transforming a legal obligation into a strategic business advantage. Successfully navigating a cybersecurity audit los angeles ensures you eliminate the technical anxiety that often accompanies state enforcement actions while building a more resilient organization.
We stand ready to serve as your expert guardian, providing the stability and peace of mind you need to thrive. Our 24/7 proactive monitoring, rapid on-site response in Los Angeles, and fixed-price unlimited IT support ensure that your systems remain secure against modern threats. Don’t let compliance hurdles slow your momentum. Your journey toward total regulatory alignment is a path to greater operational maturity and client trust.
Secure Your LA Business with a Comprehensive Cybersecurity Audit
Partner with a team that views itself as an extension of your own, dedicated to your long-term efficiency and success. We look forward to securing your digital future together.
Frequently Asked Questions
Does my small business in Los Angeles really need a cybersecurity audit in 2026?
Your small business requires a professional review in 2026 if it meets specific California thresholds or handles sensitive consumer profiles. Beyond legal mandates, audits protect you from sophisticated ransomware that frequently targets smaller firms with fewer defenses. We act as your expert guardian to ensure your infrastructure remains stable, preventing costly enforcement actions. Investing in security now replaces technical anxiety with long-term peace of mind for your team.
What is the difference between a vulnerability scan and a full cybersecurity audit?
A vulnerability scan is an automated tool that identifies known security holes in your software or network. In contrast, a cybersecurity audit los angeles is a comprehensive, human-led review of your entire digital ecosystem. It includes technical assessments, administrative policy reviews, and employee awareness testing. While a scan identifies a problem, an audit evaluates the logic behind your security strategy to ensure total regulatory compliance and long-term reliability.
How long does a typical cybersecurity audit take for an LA-based company?
A typical audit for a mid-sized Los Angeles organization usually takes between two to six weeks to complete. The timeline depends on the complexity of your network and the volume of data you process. During this period, auditors review your documentation, test your technical controls, and interview staff. We prioritize efficiency to ensure the process doesn’t disrupt your daily operations, providing a streamlined resolution that supports your business goals.
Can a cybersecurity audit help my firm comply with CCPA and CPRA?
Yes, a professional audit is the primary mechanism for demonstrating compliance with CCPA and CPRA requirements. It provides the documented evidence needed to satisfy the California Privacy Protection Agency’s Audits Division. By verifying that your data handling practices match your written privacy policies, an audit shields your firm from significant penalties. This proactive approach replaces technical anxiety with stability, positioning your organization as a trusted partner in the local community.
What happens if an auditor finds a significant vulnerability in my network?
If an auditor identifies a significant vulnerability, they provide a detailed remediation roadmap to address the flaw. This is a critical moment for proactive action rather than panic. You must implement the recommended fixes, such as patching software or updating access controls, to achieve certification. We serve as an extension of your team during this phase, using our rapid on-site response to resolve technical issues and ensure your network meets the highest standards.
How much should I budget for a professional cybersecurity audit in Los Angeles?
Budgeting for an audit depends on your organization’s size, the number of users, and the complexity of your data processing activities. Larger firms with vast cloud environments or high-risk data profiles require more intensive reviews than smaller offices. We recommend focusing on a fixed-price model to manage these costs effectively. This approach provides predictable expenses while ensuring you receive a comprehensive review that meets all 2026 California regulatory requirements without hidden fees.
Is a cybersecurity audit required for HIPAA compliance in California?
HIPAA regulations require regular risk assessments to protect patient health information, which aligns with California’s 2026 audit mandates. For healthcare providers in Los Angeles, a cybersecurity audit los angeles ensures that your technical safeguards meet both federal and state standards. This dual-layered review covers encryption, access controls, and disaster recovery protocols. Maintaining this level of compliance protects your patients’ privacy while providing the professional authority needed to navigate the complex healthcare regulatory landscape.
How often should my business undergo a third-party security review?
Most businesses should undergo a professional third-party security review at least once a year. Organizations handling high volumes of sensitive data or those subject to CalPrivacy mandates may require more frequent assessments to maintain their certified status. Regular reviews allow you to adapt to evolving threats and new regulatory updates. This consistent vigilance ensures your organization remains a step ahead of potential attackers, fostering a culture of security that supports long-term growth.