20 Sep NIST Cybersecurity Framework Implementation in Miami: A Strategic How-To
Did you know that Florida consistently ranks as the third most targeted state for cybercrime in the nation? With annual losses in our state now climbing past the $1 billion mark, the threat to your sensitive client data isn’t just theoretical; it’s a pressing business reality. You’re likely feeling the weight of potential ransomware attacks and the confusion surrounding complex federal regulations. Managing an internal security team is expensive, and finding a reliable local partner who understands the unique South Florida landscape can feel like an uphill battle.
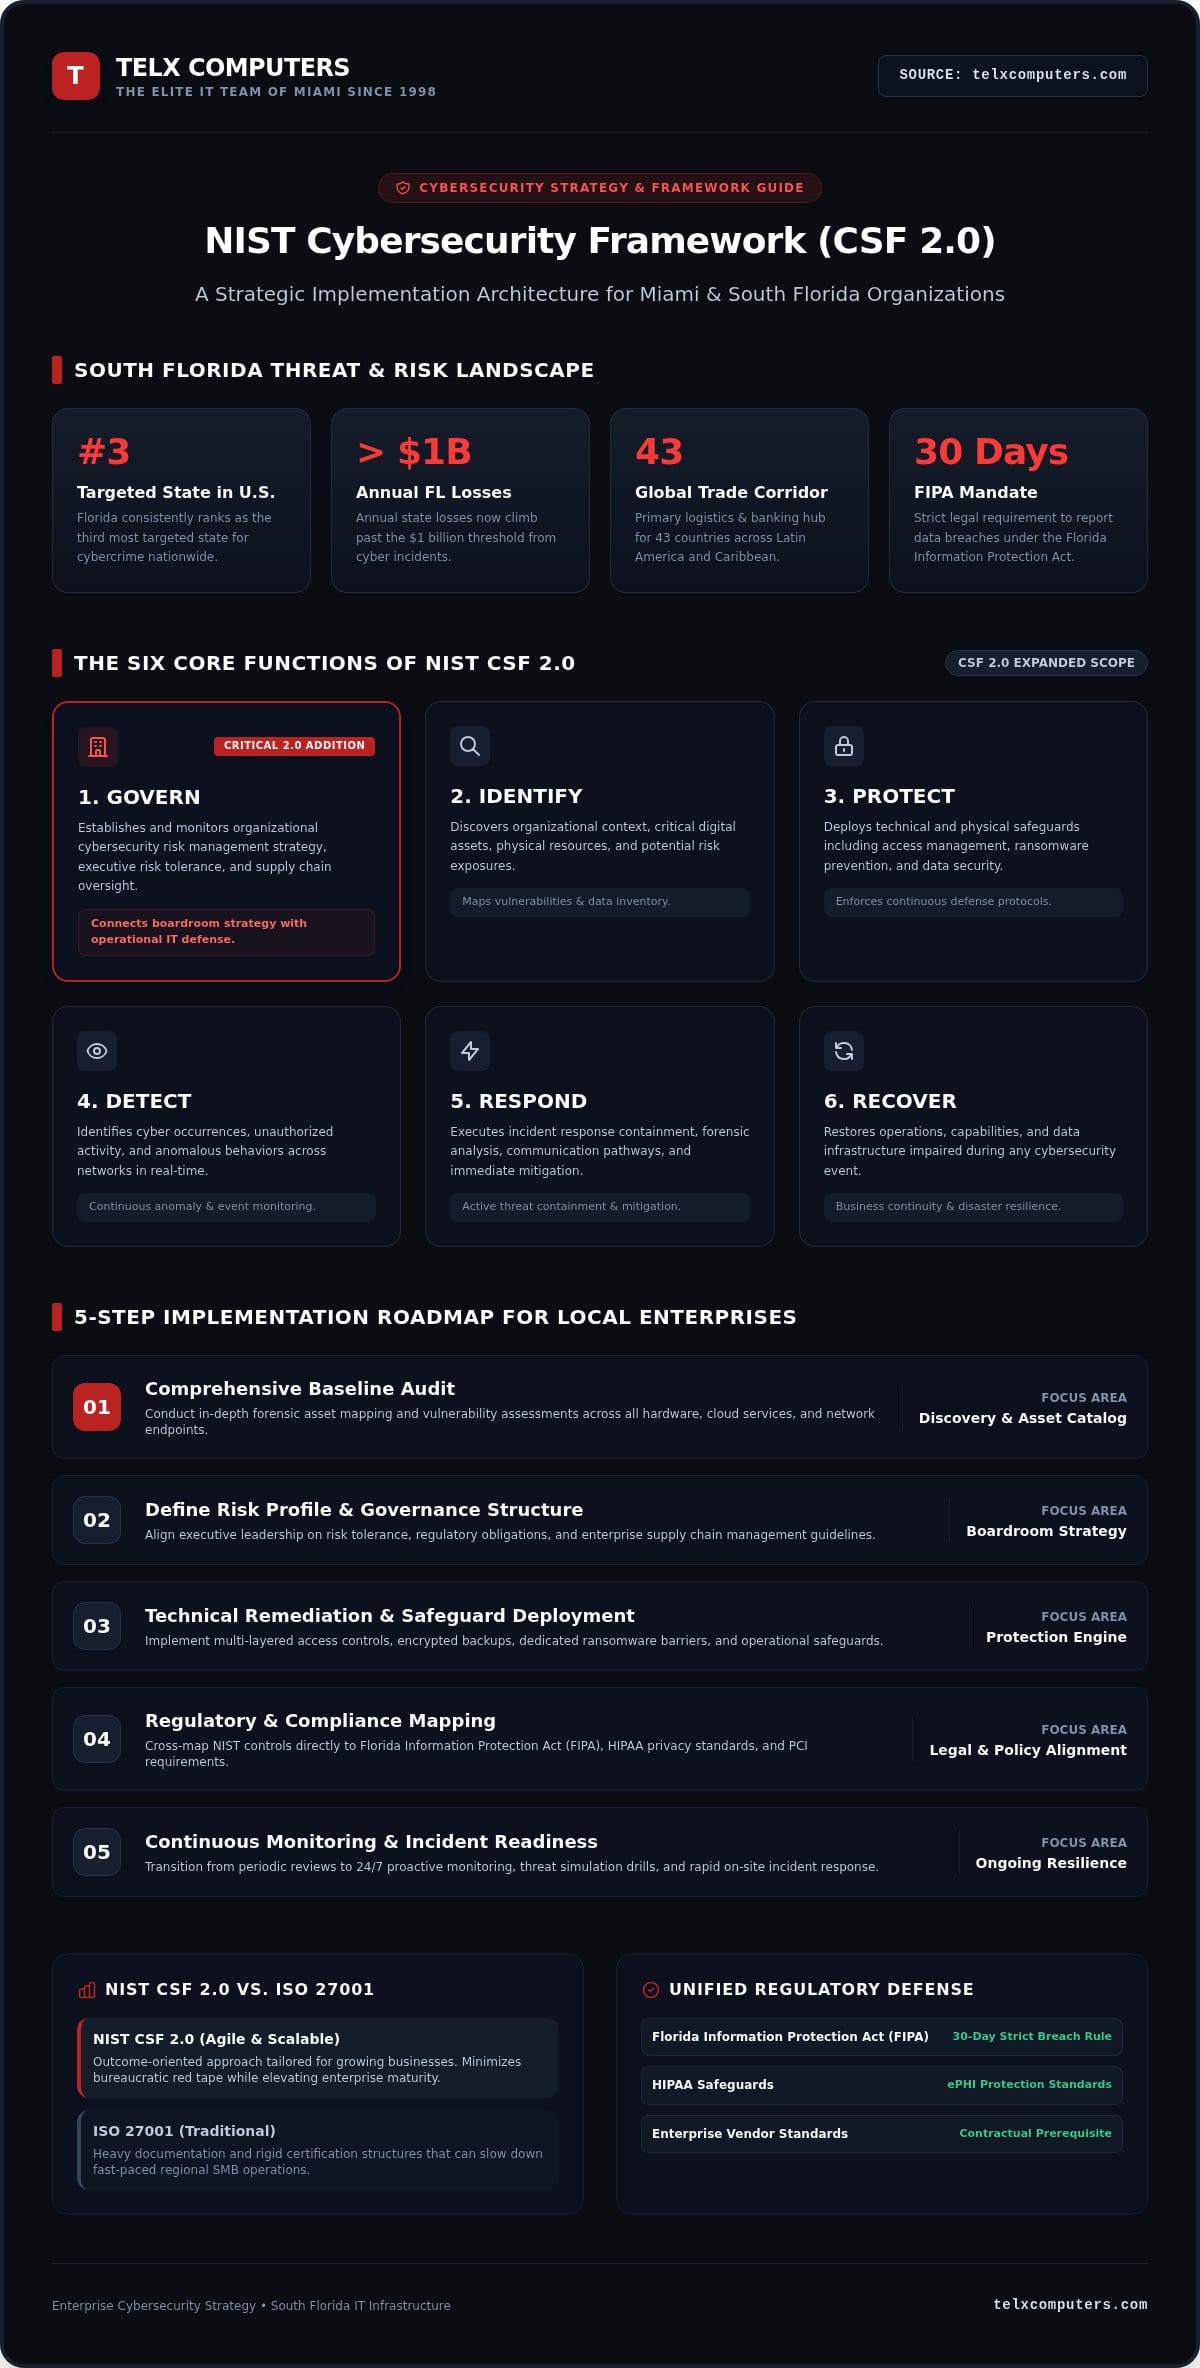
We understand that you need more than just a list of technical fixes. You need a strategic ally to handle the heavy lifting. This guide provides a clear roadmap for NIST cybersecurity framework implementation Miami, designed to move your organization toward enterprise-grade security. By following this step-by-step approach, you’ll protect your assets, satisfy compliance requirements, and potentially reduce your insurance premiums. We will break down the six core functions of NIST CSF 2.0, showing you exactly how to align your operations with global standards while maintaining a competitive edge in the Miami market.
Key Takeaways
- Understand why Miami’s unique position as a global trade hub makes NIST alignment essential for defense against rising regional cyber threats.
- Master the six core functions of NIST CSF 2.0, including the critical “Govern” function, to build a proactive security culture.
- Follow a proven, five-step roadmap for NIST cybersecurity framework implementation Miami to move from initial audit to continuous monitoring.
- Learn how NIST standards serve as a foundation for meeting strict Florida Information Protection Act (FIPA) and HIPAA requirements.
- Identify the specific criteria for selecting a local Miami security partner that provides rapid on-site response and expert guidance.
Why NIST Framework Implementation is Critical for Miami Businesses
Miami serves as the primary trade corridor for 43 countries across Latin America and the Caribbean. This status brings incredible economic opportunity, but it also places a target on your back. Cybercriminals view our city’s logistics and banking hubs as high-value targets. Choosing NIST cybersecurity framework implementation Miami changes that dynamic. It signals to the world that your business follows the same rigorous standards as federal agencies and Fortune 500 companies.
To better understand how these frameworks function in the real world, watch this helpful visual guide:
Using the NIST Cybersecurity Framework provides a common language for your entire organization. It bridges the gap between your technical team and the boardroom. When you can explain security in terms of business risk, you make better investment decisions. This alignment also creates a massive competitive advantage. Many enterprise clients and government agencies now require their vendors to demonstrate NIST compliance before signing a contract. It’s a sign of maturity that builds immediate trust with stakeholders.
The Evolving Threat Landscape in South Florida
Miami’s healthcare and legal sectors face unique pressures. You aren’t just protecting your own data; you’re safeguarding the trust of thousands of clients. For a local SMB, the average cost of a breach involves forensic audits, legal fees, and long-term reputational damage. Florida law is strict. Under the Florida Information Protection Act, you must report breaches within 30 days or face heavy penalties. Traditional “good enough” security can’t keep up with modern threats. You need a dedicated ransomware protection strategy that treats security as a continuous process rather than a one-time project.
NIST vs. Other Frameworks: Why it Wins
While ISO 27001 is a solid standard, it often feels overly bureaucratic for fast-moving Miami firms. NIST CSF 2.0 is different. It’s designed to be scalable and outcome-oriented. It fits perfectly with Managed IT Services in Miami because it allows for customization based on your specific risk profile. Whether you’re a small logistics firm or a large financial office, NIST provides a roadmap that grows with you. It’s the most reliable way to ensure your security posture remains robust without suffocating your operations with unnecessary red tape or complex federal jargon.
Understanding the NIST Cybersecurity Framework (CSF 2.0)
The NIST Cybersecurity Framework (CSF) isn’t a rigid set of rules that forces your business into a one-size-fits-all box. Instead, it’s a voluntary collection of standards and best practices designed to help organizations manage and reduce risk. For local leaders embarking on a NIST cybersecurity framework implementation Miami journey, the update to CSF 2.0 is a significant milestone. It expands the official scope from critical infrastructure to organizations of all types and sizes, making it an accessible tool for the entire South Florida business community.
The most vital shift in the official NIST CSF 2.0 guidance is the introduction of the “Govern” function. This sixth core function emphasizes that cybersecurity isn’t just a technical task for the server room; it’s a high-level business strategy. It requires executives to define organizational risk tolerance and supply chain risk management. By integrating security into the boardroom, you ensure that every technical safeguard supports your broader corporate objectives.
The Six Core Functions of NIST
The framework organizes its activities into six key areas that provide a holistic view of your security posture. Success of your NIST cybersecurity framework implementation Miami project depends on balancing these functions.
- Identify & Govern: These functions focus on understanding your business context, the physical and software assets you own, and the governance policies that guide your team.
- Protect & Detect: This is where you build your defenses. You implement safeguards like access control and data security, while simultaneously monitoring for unauthorized activity.
- Respond & Recover: These functions ensure you have a battle-tested plan to contain an incident and restore any services that were impaired, minimizing downtime and data loss.
How NIST Tiers Help Your Business Grow
The framework uses “Implementation Tiers” to help you measure maturity. They range from Tier 1 (Partial), where risk is managed in an ad hoc manner, to Tier 4 (Adaptive), where your organization proactively learns from the evolving threat landscape. Most Miami firms aiming for enterprise-grade security should target Tier 3 (Repeated), where risk management practices are formally approved and expressed as policy.
Mapping these tiers to your business goals allows you to prioritize investments where they’ll have the most impact. If you’re unsure where your current maturity level sits, a professional managed IT support service can help you conduct a gap analysis to find your starting point. NIST CSF 2.0 is the strategic blueprint for modern cyber-resilience.
5-Step How-To Guide for NIST Implementation in Miami
Moving from high-level theory to practical application requires a structured approach. A successful NIST cybersecurity framework implementation Miami project follows five distinct phases. This methodology ensures that your security investments align with your operational needs while addressing the specific threats found in South Florida’s business environment. By breaking the process into manageable steps, you remove the technical anxiety often associated with federal standards.
Step 1: The Foundation of Asset Management
You can’t protect what you don’t know exists. The first step involves a deep dive into every hardware device, software application, and data repository in your network. This is particularly challenging for Miami’s hybrid workforces where “Shadow IT”, unauthorized apps or personal devices used for work, is common. Utilizing robust Server Monitoring Systems allows you to maintain a real-time inventory of your critical infrastructure, ensuring no asset remains invisible to your security team.
Step 2 involves creating a Target Profile. This profile describes your desired cybersecurity outcomes based on your industry’s standards and your organization’s risk appetite. It serves as the “North Star” for your entire implementation journey, allowing you to visualize exactly what a secure state looks like for your specific firm.
Step 3: Bridging the Security Gap
Once you have your current and target profiles, you must perform a gap analysis. This process isn’t just about finding technical flaws; it’s about ranking vulnerabilities by their potential business impact. In Miami, phishing and credential theft remain the top entry points for attackers. Addressing these through multi-factor authentication and employee training is essential. You should also prioritize Ransomware Protection to ensure that a single compromised account doesn’t lead to a total operational shutdown. By focusing on high-impact gaps first, you maximize your return on investment.
Step 4 is the Execution of the Implementation Plan. This is where your team or your strategic partner remediates the identified gaps. It involves updating policies, deploying new technologies, and refining incident response playbooks according to the NIST Cybersecurity Framework. This phase turns your strategy into a functional shield.
Step 5: Proactive Vigilance
Cybersecurity isn’t a project with a finish line; it’s a continuous cycle of improvement. Threats evolve, and so must your defenses. Establishing a monitoring loop is critical for the “Detect” and “Respond” functions of NIST. This is where 24/7 help desk support becomes invaluable, providing the constant eyes-on-glass needed to catch anomalies before they escalate. You should review your profiles annually, or whenever your business undergoes a major change, like an acquisition or a shift to new cloud platforms. This proactive stance keeps your organization resilient against the next generation of threats.
Compliance Alignment: HIPAA, PCI, and Florida Privacy Laws
Compliance isn’t just about avoiding fines; it’s about building a foundation of trust with your clients. For many organizations, NIST cybersecurity framework implementation Miami serves as the primary engine for satisfying multiple regulatory bodies simultaneously. Because the NIST categories map directly to the requirements of HIPAA, PCI DSS, and the Florida Information Protection Act (FIPA), you don’t have to build separate security silos for each mandate. This unified approach ensures that your defense strategy is as efficient as it is effective.
The Florida Information Protection Act (§ 501.171) requires businesses to report data breaches to affected residents within 30 days. Meeting this tight window is nearly impossible without the “Respond” and “Recover” playbooks defined within the NIST framework. By aligning with these standards, you ensure that your incident response team knows exactly how to identify, contain, and report a breach before the legal clock runs out. It turns a chaotic emergency into a controlled, documented process.
NIST for Miami Law Firms and Healthcare Providers
Protecting Personally Identifiable Information (PII) and Protected Health Information (PHI) is a non-negotiable duty for local practices. Implementing Healthcare IT Services in Miami according to NIST standards provides a “Recognized Security Practice” that the HHS Office for Civil Rights considers when mitigating fines during breach investigations. Similarly, IT Services for Law Firms must prioritize client confidentiality. NIST controls for access management and encryption ensure that sensitive case files remain shielded from unauthorized eyes, satisfying both ethical obligations and statutory requirements.
Automating Compliance with Managed Services
The administrative burden of manual compliance is a significant drain on resources. Real-time monitoring replaces the stress of annual audits by providing a continuous stream of documentation. When your systems are aligned with NIST, you can generate reports for auditors that prove your security posture at any given moment. This level of transparency is essential for Miami retail and e-commerce businesses that must now adhere to PCI DSS v4.0.1 standards, which became mandatory on March 31, 2025. NIST alignment simplifies multi-regulatory compliance by providing a single, unified set of controls that satisfy the most rigorous federal and state auditors.
To see how your current security measures stack up against these requirements, request a professional cybersecurity audit today.
Selecting a Miami Cybersecurity Partner for NIST Alignment
Selecting the right partner for NIST cybersecurity framework implementation Miami is a decision that defines your organization’s resilience. You aren’t just hiring a vendor; you’re choosing a strategic ally to handle the technical heavy lifting while you focus on growth. A common dilemma for local firms is the “buy vs. build” comparison. Building an internal cybersecurity department requires significant capital for salaries, benefits, and constant training. For most SMBs, this is a massive financial burden. Partnering with a specialized provider gives you immediate access to a high-tier corporate department’s resources at a fraction of the cost, making enterprise-grade security predictable and affordable.
When evaluating a potential partner, look for a firm that treats NIST as a holistic strategy rather than a series of disconnected fixes. A NIST-ready partner must demonstrate a deep understanding of the “Govern” function, linking technical controls directly to your operational needs. During your IT Consultation, ask how they manage asset inventory and whether they offer the 24/7 visibility required for modern compliance. The right partner acts as the silent engine behind your success, ensuring you stay one step ahead of potential threats.
Why Local Miami Support is Essential
Miami’s business culture is fast-paced and unique. Whether your office is in Aventura, downtown Miami, or Fort Lauderdale, having a partner who understands the local landscape is vital. For the “Recover” function of the NIST framework, rapid on-site response isn’t just a luxury; it’s a necessity. If a physical hardware failure or a massive network breach occurs, you need a team that can be on the ground in minutes, not hours. Local expertise ensures your partner is familiar with regional threat actors and Florida-specific data laws, allowing them to act as a seamless, proactive extension of your own team.
The Telx Advantage: Strategic Cybersecurity
At Telx Computers, we integrate NIST principles directly into our Managed IT Support Services. We believe that top-tier security shouldn’t come with unpredictable costs. Our fixed-price, unlimited service plans eliminate the anxiety of the “billable hour,” allowing us to focus on long-term alignment rather than short-term fixes. This model supports a continuous improvement cycle, ensuring your defenses evolve as fast as the threats. Our Service Guarantee provides the reliability you can bank on, giving you the peace of mind to grow your business with confidence.
Future-Proof Your Miami Enterprise Today
Securing your organization against the rising tide of cyber threats requires more than just reactive software. It demands a holistic strategy that bridges the gap between technical safeguards and business governance. By committing to NIST cybersecurity framework implementation Miami, you aren’t just checking a compliance box; you’re building a foundation of trust that protects your sensitive client data and ensures long-term operational resilience. You now have the roadmap to move from an initial audit to a state of continuous, adaptive defense.
Success in this landscape depends on having a vigilant guardian by your side. With over 20 years of local South Florida expertise, we provide the 24/7 Miami-based SOC monitoring and fixed-rate predictable IT budgeting you need to maintain a technological edge. Don’t let the complexity of federal regulations or the fear of ransomware stall your growth. It’s time to replace technical anxiety with the peace of mind that comes from professional reliability.
Secure Your Miami Business with a NIST Alignment Audit. We’re ready to act as your strategic ally, ensuring your company remains one step ahead of every threat.
Frequently Asked Questions
Is NIST implementation mandatory for private businesses in Miami?
NIST implementation is voluntary for most private organizations in Florida, but it remains the gold standard for demonstrating reasonable security. While private firms aren’t legally forced to adopt it, Florida statutes now mandate that local governments align their standards with the framework. For Miami businesses, adopting NIST acts as a legal safe harbor under FIPA and provides a recognized defense strategy that satisfies federal auditors and enterprise clients alike.
How long does a typical NIST implementation take for a small business?
A full NIST cybersecurity framework implementation Miami project typically spans six to twelve months for total maturity. However, we often see significant security improvements within the first thirty to ninety days. This initial phase focuses on the Identify and Protect functions, establishing a baseline and securing critical assets. The timeline depends on your current implementation tier and the complexity of your existing network infrastructure in South Florida.
Can my current internal IT team handle NIST implementation alone?
While internal teams are excellent at daily operations, NIST implementation requires specialized cybersecurity expertise that goes beyond general IT maintenance. Most internal departments lack the time and tools to conduct the deep-dive audits and continuous monitoring the framework demands. We act as a strategic ally, handling the technical heavy lifting and governance documentation. This allows your internal staff to stay focused on core business projects while we secure the perimeter.
How does NIST CSF 2.0 differ from the original framework?
The most significant change in NIST CSF 2.0 is the addition of the Govern function, which elevates cybersecurity from a technical task to a boardroom priority. This update also officially expands the framework’s scope to include organizations of all sizes and sectors, not just critical infrastructure. For a Miami business, this means the framework is now more flexible and focuses on how security policies integrate with your overall corporate risk management strategy.
What are the costs associated with NIST implementation in Miami?
Costs for NIST alignment vary based on your organization’s size and current security gaps. Typical expenses include the initial audit, specialized software licenses, and ongoing managed monitoring. We help Miami firms manage these costs through our fixed-price, unlimited service plans. This model removes the fear of hourly billing, making the transition to a high-tier security posture both predictable and affordable for your annual budget without hidden fees.
Will implementing the NIST framework slow down our employees?
Implementing the framework doesn’t have to hinder your team’s productivity. In fact, many NIST-aligned controls, such as single sign-on and hardware-bound authentication, actually simplify the user experience. By streamlining access management and reducing the risk of downtime from breaches, your employees can work more efficiently. We focus on being the silent engine behind your success, deploying security measures that protect your data without creating unnecessary friction in your daily operations.
How often do we need to audit our NIST alignment?
We recommend conducting a formal NIST alignment review at least once every twelve months. However, the framework’s Detect and Respond functions require continuous monitoring to be truly effective. Major business changes, such as migrating to the cloud or opening new offices in Aventura or Fort Lauderdale, should also trigger a fresh audit. Our proactive server monitoring ensures that your security posture remains adaptive to new threats between these formal annual assessments.
How does NIST help with cyber insurance applications in Florida?
Cyber insurance carriers in Florida increasingly require proof of framework alignment before approving coverage or offering competitive rates. By demonstrating a mature NIST implementation, you provide the documentation insurers need to see that you’ve mitigated common risks like ransomware. This proactive stance often leads to reduced premiums and higher coverage limits. We act as your expert guardian, providing the reporting and technical proof required to satisfy even the most rigorous insurance underwriters.